Security built into every layer
Client accounts, staff access and money movement are protected by design, from the first login to the last withdrawal.
Protecting client accounts
Two-step sign-in
Email one-time codes on login, plus optional authenticator-app 2FA.
Login throttling
Repeated failed logins lock by IP and identifier.
Security Centre
Clients see login history and devices, and manage trusted devices.
Anti-phishing phrase
A personal phrase in every email so clients can spot fakes.
Withdrawal allowlist
Crypto withdrawals go only to allowlisted addresses, with a delay after changes.
Single-use reset links
Password resets use one-time tokens that expire after an hour.
Protecting your operation
IP-allowlisted CRM
The back office only opens from approved IP addresses.
Roles & lead scoping
Page-level permissions, lead scoping and agent IP checks.
Actor-aware audit log
Every action is recorded with who did it: admin, agent or client.
CSRF protection
Tokens on every form in the client portal.
Secrets out of code
Credentials live in environment configuration, never in source.
Protected origin
Servers sit behind a protected network edge, with admin access over a private network.
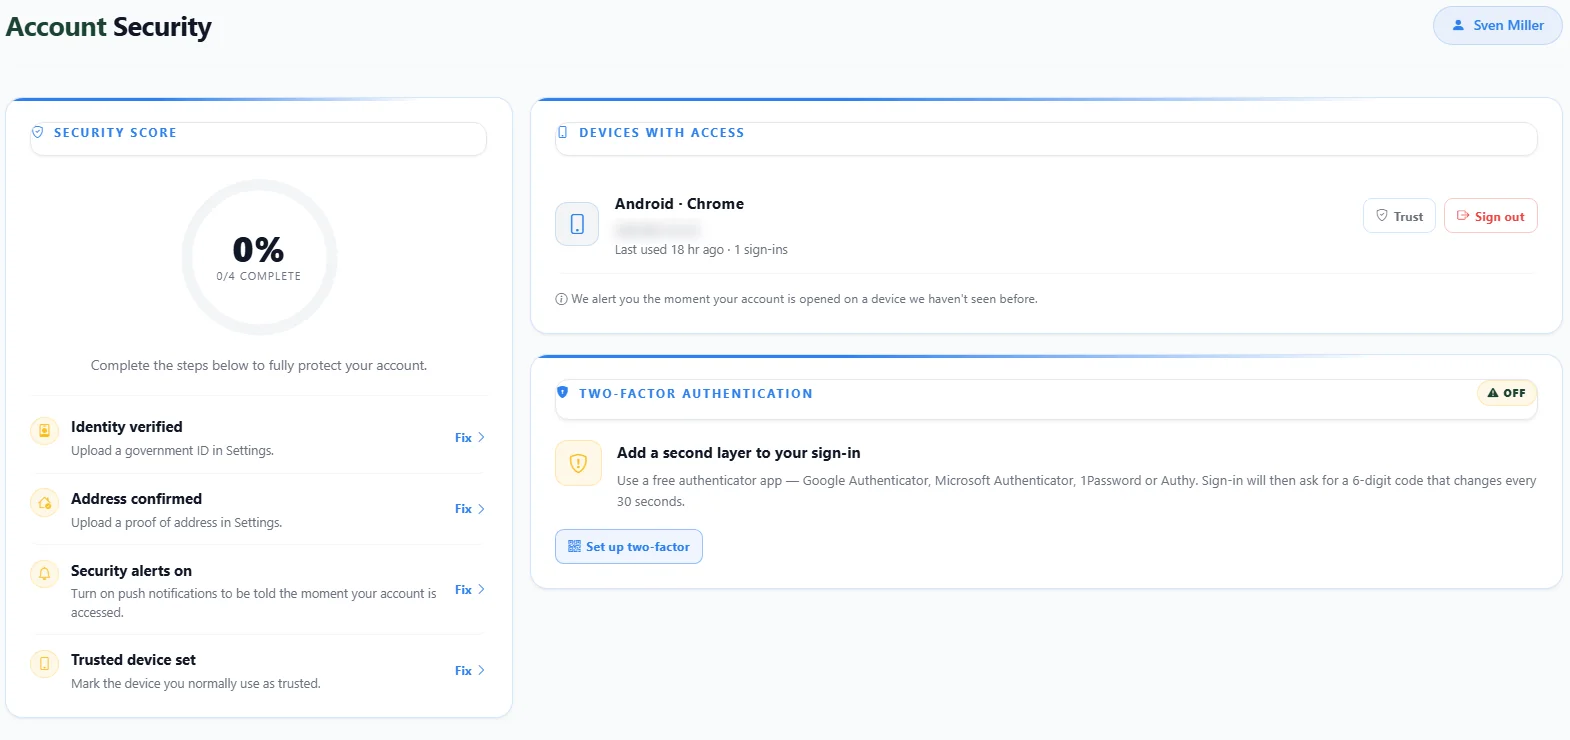
Clients can see and control their own security
A security score guides clients through identity checks, alerts and trusted devices. Every device with access is listed and can be trusted or signed out.
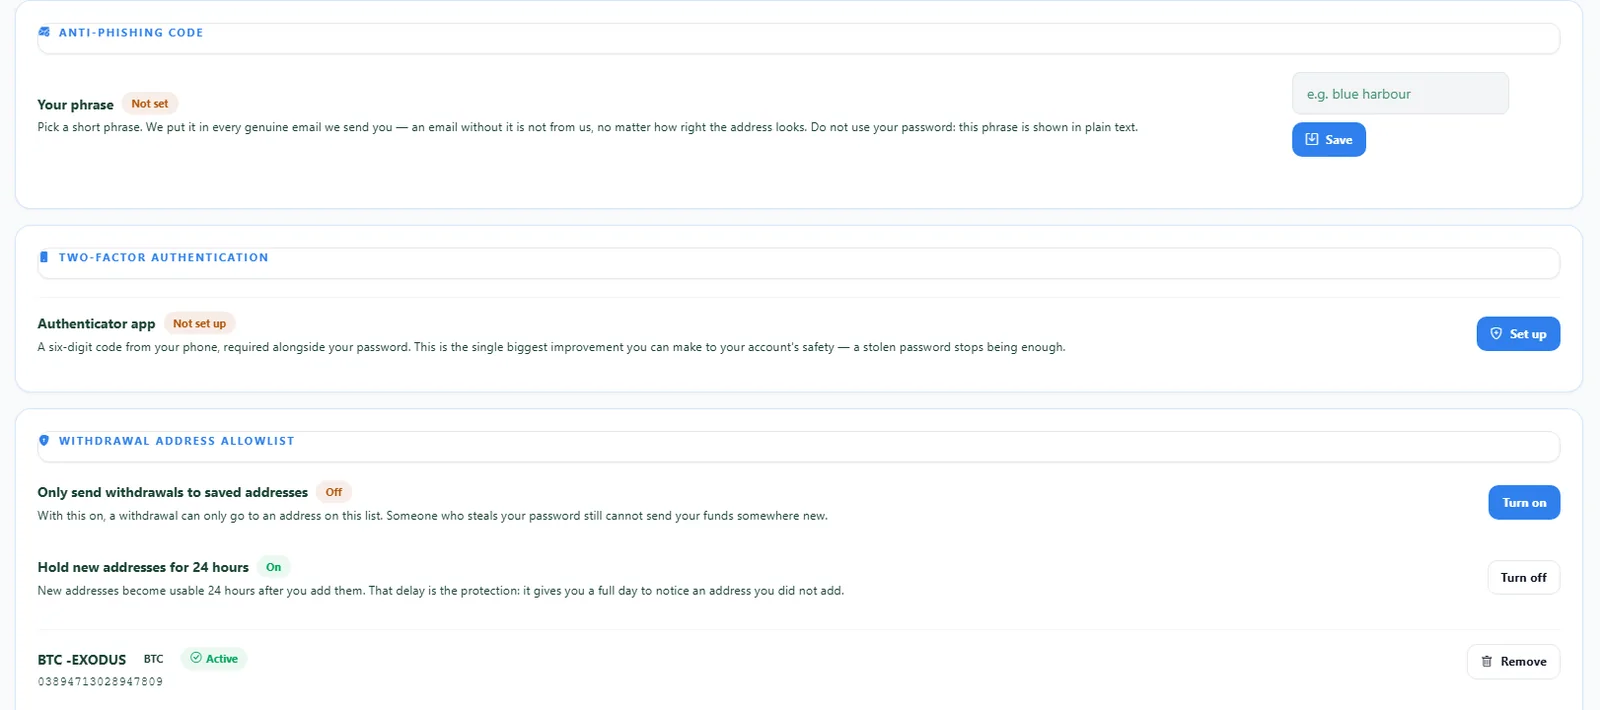
Anti-phishing phrase, 2FA and address allowlist
Clients set a phrase that appears in every genuine email, turn on authenticator-app 2FA, and restrict withdrawals to saved addresses with a 24-hour hold on new ones.
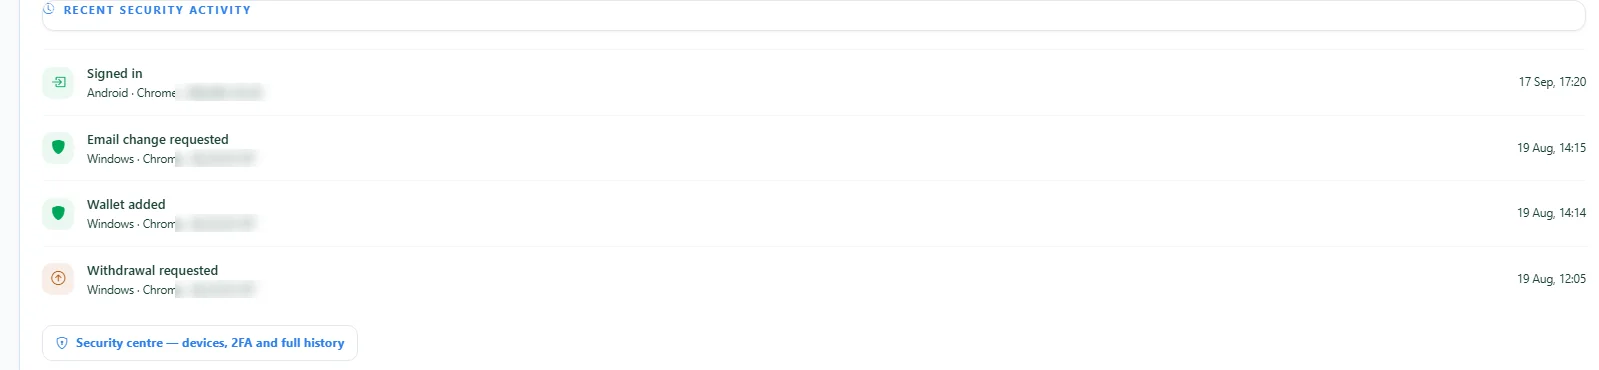
Every sensitive action is logged
Sign-ins, email changes, new wallets and withdrawal requests appear in the client's security activity, with device and time.
Questions about security? Ask us in the demo.
We will walk you through the CRM, WebTrader and client portal live, discuss pricing for your setup, and plan your launch.